Tag: Business – Decrypt

  • Vitalik Buterin Says Ethereum Is Betting Its Future on Quantum Security and AI

    Vitalik Buterin Says Ethereum Is Betting Its Future on Quantum Security and AI

    In brief

    • Vitalik Buterin says Ethereum has elevated quantum security and privacy since its 2023 roadmap.
    • Ethereum researchers are increasingly relying on STARKs and AI-assisted formal verification.
    • The roadmap also includes native rollups and explores a future beyond the EVM.

    Ethereum co-founder Vitalik Buterin says quantum resistance, privacy, and AI-assisted security have become greater priorities for Ethereum since he published his 2023 roadmap.

    In a post on X on Monday, Buterin said he updated his 2023 roadmap to compare its original goals with Ethereum’s current “Strawmap”—a working outline of the network’s long-term technical priorities.

    “What’s most striking, however, is that some completely new things are in the strawmap that are not in this diagram, because they were not in the 2023 roadmap at all,” Buterin wrote. “These reflect changing priorities.”

    Among those priorities are stronger privacy and scaling designed for a post-quantum world, alongside efforts to push the “lean-ification of the spec,” or simplify Ethereum’s technical specifications.

    “A common theme in scaling, found in both state types and zkzk frames (both new ideas), is that instead of trying to maximally scale all Ethereum activity,” Buterin wrote. “We try to create specialized mechanisms that have more restrictive properties that make them more scaling-friendly, while supporting the heaviest loads incurred by users and applications today (eg. token transfers, swaps) and tomorrow (eg. privacy protocols).”

    According to Buterin, advances in AI are making it practical to apply the technique more extensively to Ethereum.

    Buterin said Ethereum is increasingly relying on STARKs, a cryptographic technology used to verify computations, and AI-assisted verification, to check that the protocol works as intended.

    “This can only be safe with formal verification, which is itself only feasible with modern AI tools,” he wrote.

    Buterin’s post comes as Ethereum has accelerated preparations for “Q-Day” and the potential threat posed by quantum computers.

    In January, Buterin urged developers to adopt quantum-resistant cryptography before the threat becomes immediate, and the Ethereum Foundation formed a dedicated post-quantum team. In February, Buterin outlined a phased plan to replace four potentially vulnerable components of Ethereum’s cryptographic architecture.

    In July, Buterin put quantum safety and privacy at the center of his proposed “Lean Ethereum” overhaul, which calls for replacing quantum-vulnerable cryptography with quantum-safe alternatives.

    “Ethereum will be quantum-safe. Ethereum will put users’ privacy first. Ethereum will be secure,” Buterin wrote. “Ethereum will be censorship-resistant. Ethereum will be highly performant and scalable while satisfying the above. And Ethereum will be Lean.”

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • Standard Chartered Sees $4T Tokenization Driving Chainlink to $200 by 2030

    Standard Chartered Sees $4T Tokenization Driving Chainlink to $200 by 2030

    In brief

    • Standard Chartered initiated coverage of Chainlink on Monday with a price target of $200 by end-2030, up from around $8 today.
    • The bank expects tokenized assets on-chain to reach $4 trillion by end-2028 and assets deployed in DeFi to grow 37-fold to $2.7 trillion by 2030.
    • LINK was trading at around $8.25 Monday, down 0.8% on the day, according to CoinGecko.

    Standard Chartered has initiated coverage of Chainlink with a price target of $200 by the end of 2030, implying a roughly 25-fold gain from around $8 today and outperformance of both Bitcoin and Ethereum over the period.

    Geoff Kendrick, the bank’s global head of digital assets research, laid out staged targets in a note published Monday: $13 by the end of this year, then $41, $82 and $133 before reaching $200. The same note pencils in Bitcoin at $500,000 and Ethereum at $40,000 by end-2030.

    Kendrick expects the value of tokenized assets on-chain to climb roughly 12-fold to $4 trillion by end-2028 from about $340 billion now, and assets deployed in DeFi to grow 37-fold to $2.7 trillion by 2030. Because Chainlink charges for delivering data and moving assets between chains, the bank estimates its fees should rise about 25 times over that period, and assumes the token price follows fees.

    Chainlink’s incumbency is the other half of the argument. The note puts its total value secured above $110 billion, covering roughly 70% of oracle-dependent value in DeFi globally and more than 80% on Ethereum. Aave V3 alone accounts for 44% of that secured value.

    Wall Street on the client list

    Kendrick named Swift, DTCC, Euroclear, JP Morgan, Mastercard, UBS, Fidelity and S&P Global among institutions using Chainlink services, and expects off-chain customers to become a growing share of fees. Tokenized funds and bonds need net asset values, rates and reserve attestations, making them more data-hungry than crypto-native assets.

    On interoperability, Chainlink still trails LayerZero. The note says more than $7 billion in token value has moved from legacy bridges to Chainlink’s CCIP since a $292 million exploit in April, with quarterly CCIP volume reaching $4.9 billion in the second quarter, up 353% year on year. Decrypt reported in May that KelpDAO blamed LayerZero for that exploit and planned to rebuild on Chainlink, a characterization LayerZero disputes.

    The note is the latest in a run of DeFi initiations from Kendrick, all built on the same 37-fold forecast. He set targets of $100 for Uniswap and $3,500 for Aave in June, and $60 for Morpho in July. UNI jumped double digits after its note landed. Chainlink’s response has been more muted, with LINK currently trading at $8.25, down 0.8% on the day, per CoinGecko data.

    Risks flagged in the note include institutional tokenization scaling more slowly than expected, pilots failing to become recurring production workflows, specialist providers taking share, and technical failures denting confidence.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • Bitcoin ‘Anti-Spam’ Fork Sputters to a Halt After Mining Just Two Blocks

    Bitcoin ‘Anti-Spam’ Fork Sputters to a Halt After Mining Just Two Blocks

    In brief

    • Supporters of BIP-110 split off into a minority Bitcoin chain on Saturday at block 961,632, but it mined only two blocks in about eight hours before stalling, falling dozens of blocks behind the main network.
    • The fork inherited Bitcoin’s difficulty setting with barely any hashpower—about 2.53% of recent blocks signaled support, far below the 55% activation threshold,
    • BIP-110 sought to temporarily block non-financial data like Ordinals inscriptions from transactions, a move critics including Michael Saylor call a dangerous precedent.

    The long-simmering fight over a controversial Bitcoin network proposal finally produced a chain split over the weekend, but the breakaway Bitcoin fork sputtered almost immediately, grinding out just two blocks in roughly eight hours before stalling out.

    The fork came as a result of a Bitcoin Improvement Proposal known as BIP-110, whose supporters claimed would protect the network from unwanted spam and the legal liability that comes from hosting non-financial data on the network. Its detractors, the majority of the Bitcoin community, viewed it as an attempt at censorship.

    The fork triggered Saturday at block 961,632, when Bitcoin nodes running BIP-110 software began rejecting any block that failed to signal support for the proposal. A block mined by AntPool without that signal was accepted by the main network and rejected by BIP-110 nodes, while a miner on the Ocean pool produced the alternative the minority chain followed.

    Hours later, the splinter chain sat far behind, trailing the main network by dozens of blocks as Bitcoin kept churning out one roughly every ten minutes.

    The stall stems from a problem the fork can’t easily escape. Bitcoin only recalibrates its mining difficulty every 2,016 blocks, and the breakaway chain inherited the network’s current setting while commanding a sliver of its computing power—about 2.53% of recent blocks signaled for the proposal, far short of the 55% needed to activate without splitting. At that pace, the chain would need roughly 350 days to reach its next difficulty adjustment, versus about two weeks for Bitcoin, leaving blocks hours apart.

    BIP-110, as Decrypt has previously reported, is a soft-fork proposal to temporarily bar people from stuffing images, text, and other non-financial data into Bitcoin transactions. Backers argue the practice, popularized by Ordinals inscriptions, clogs the network and drives up fees for ordinary payments.

    Opponents counter that anyone paying for block space has earned the right to use it as they see fit, and that letting miners and node operators police transactions erodes Bitcoin’s censorship resistance. Strategy’s Michael Saylor has been among the critics, warning that turning a spam dispute into a consensus change sets a dangerous precedent.

    On early Sunday morning, Saylor posted on X: “Bitcoin worked exactly as designed. BIP-110 was free to fork, and the network was free not to follow. The result was decisive: about 99.85% of Bitcoin’s hash power stayed with Bitcoin. The BIP-110 branch mined only two blocks and is already more than 80 blocks behind.”

    Jameson Lopp, a long-time Bitcoin advocate and the co-founder of Bitcoin security company Casa, echoed the sentiment and took it a step further: I won’t be ‘welcoming back’ or unblocking any BIP-110 supporters,” he posted on X. “They proved themselves to be susceptible to delusional propaganda from folks emanating reality distortion fields. In many cases they spewed vitriol and harassed the very people who have devoted their lives to supporting and improving Bitcoin.”

    There’s a further catch for anyone holding the fork’s coins: because both chains accept identical transactions, a sale on the minority chain can be replayed on Bitcoin, potentially handing a buyer real BTC from the same seller. The mandatory signaling window closes at block 963,647—a mark the chain won’t come close to reaching.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • Bitcoin Red Team Says AI Is Finding Critical Exploits Across Core Projects

    Bitcoin Red Team Says AI Is Finding Critical Exploits Across Core Projects

    In brief

    • The initiative says it has scanned about 150 Bitcoin repositories and made more than a dozen vulnerability disclosures.
    • The team is developing an open-source AI platform for auditing Bitcoin software.
    • Developers say the effort is uncovering critical vulnerabilities across wallets, cryptographic libraries, and infrastructure.

    A volunteer security initiative says it used frontier AI models to scan 150 Bitcoin repositories and found more than a dozen vulnerabilities as developers increasingly use artificial intelligence to audit blockchains.

    In a post on X earlier this week, AnchorWatch CEO Rob Hamilton said the group has spent about $20,000 on AI services while building a “Bitcoin red team” platform.

    “We have been working around the clock, with ~$20,000 of spend up to this point across different services,” he wrote. “Funding is secured, I appreciate all the gestures for donations but it is not necessary. The bill is taken care of.”

    A red team refers to cybersecurity professionals who test software from an attacker’s perspective, probing for vulnerabilities before they can be exploited.

    According to Hamilton, the Bitcoin red team uses Kimi K3 alongside OpenAI’s GPT Sol, Anthropic’s Claude Fable and Opus models, and Z.ai’s GLM 5.2 to identify vulnerabilities and generate supporting documentation.

    “We also have been connected with OpenAI for some help so I could manage getting the Cyber Harness running as well,” he wrote. “It’s a much more expensive scan, but well worth it for load-bearing portions of the Bitcoin ecosystem and has already yielded good results.”

    Pseudonymous Bitcoin developer Calle said the initiative has built multiple AI-powered review systems targeting wallets, cryptographic libraries, infrastructure, and other Bitcoin projects.

    “We’re averaging on the order of one critical exploit per hour per person,” Calle wrote on X. “We’ve reported critical vulnerabilities to several projects in the last 12 hours. Thankfully, this is a very expensive exercise. We’re burning through $10,000 per day.”

    The team did not disclose which projects were affected or provide details of the vulnerabilities.

    The announcement comes as AI is playing a growing role in finding security flaws across the crypto industry. Earlier this year, researchers using Anthropic’s Claude Opus 4.8 uncovered a four-year-old flaw in Zcash that could have allowed attackers to create unlimited counterfeit ZEC. In August, Coinkite said it believes attackers used AI to identify the Coldcard wallet vulnerability, while Bitcoin bridge Boltz suspended its swap service after saying attackers were using AI to identify vulnerabilities faster than its team could patch them.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • Trump Media Abandons Crypto Treasury, Prediction Market Ventures

    Trump Media Abandons Crypto Treasury, Prediction Market Ventures

    In brief

    • Trump Media has ended plans for a Crypto.com-backed CRO treasury company.
    • The companies also scrapped a broader digital asset deal and scaled back prediction market plans.
    • Existing Truth Social Funds ETFs will continue unchanged.

    President Donald Trump’s Trump Media & Technology Group has scrapped plans to launch a Crypto.com-backed CRO treasury company and abandoned a broader digital asset deal with the company.

    According to a report by Axios, Trump Media, Crypto.com, and special purpose acquisition company Yorkville Acquisition Corp. have mutually agreed to terminate the proposed Trump Media Group CRO Strategy, a previously announced services agreement, and related digital asset products.

    The companies cited “prevailing market conditions” and “shifting business and stakeholder priorities” for the decision.

    The venture would have licensed the Trump Media name for a company built around Crypto.com’s Cronos blockchain and the Cronos token, which trades as CRO. When announced last year, the partners said it would become the first and largest publicly traded CRO treasury company by accumulating the token and generating additional returns from those holdings. The CRO token currently trades for $0.05, falling sharply following the news, at around a $2.4 billion market capitalization.

    Interim CEO Kevin McGurn told Axios the company is narrowing its focus after the market for digital asset treasury companies became increasingly crowded over the past year. He added that staking has become less important to Crypto.com, making it the right time for the companies to go their separate ways.

    The Truth Social parent company is also abandoning plans to integrate prediction markets directly into Truth Social. Instead, the companies will pursue a marketing deal that promotes Crypto.com’s prediction market products to Truth Social users.

    McGurn said the prediction market business has become crowded, making it a less compelling area for investment. Rather than operating prediction markets itself, Trump Media now sees greater value in acting as a distribution and data partner.

    Trump Media’s relationship with Crypto.com had expanded over the past year.

    In October 2025, Trump Media announced plans to launch Truth Predict, a Crypto.com-powered prediction market integrated with Truth Social. In December, the companies unveiled plans for a publicly traded CRO treasury company with Yorkville Acquisition Corp., which was expected to hold billions of CRO tokens. In February, Crypto.com disclosed donating $35 million over the previous year to the pro-Trump super PAC MAGA Inc. The same month, the Office of the Comptroller of the Currency conditionally approved the exchange’s application for a national trust bank charter.

    Democrats have repeatedly criticized Trump’s expanding crypto ventures.

    Earlier this week, Sen. Elizabeth Warren (D-Mass.) and Sen. Richard Blumenthal (D-Conn.) urged the SEC to investigate President Donald Trump’s meme coin, arguing the agency should determine whether it facilitated fraud or unjust enrichment. The request is the latest sign of growing Democratic scrutiny of Trump’s business dealings, specifically in crypto, ahead of November’s midterm elections.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • MyTrade Founder Fined $10K Over Bots That Wash Traded 60 Cryptocurrencies

    MyTrade Founder Fined $10K Over Bots That Wash Traded 60 Cryptocurrencies

    In brief

    • MyTrade founder Liu Zhou has been fined $10,000 over running a crypto wash trading service.
    • Zhou pleaded guilty in October 2024 alongside 17 co-conspirators charged in the same operation.
    • MyTrade’s dashboard let clients order a daily volume of fake trades, executed by bots.

    The founder of crypto market maker MyTrade has avoided prison and been fined $10,000 for running a wash trading service that generated millions of dollars in fake daily volume across roughly 60 cryptocurrencies.

    Liu Zhou, 41, a Canadian citizen and Chinese national, was sentenced in Boston federal court on Thursday by U.S. District Judge Angel Kelley, who imposed no custodial term, Law360 reported. He pleaded guilty to conspiracy to commit market manipulation and wire fraud after being charged in October 2024 alongside 17 other individuals and entities.

    MyTrade sold the service openly. Clients logged into a dashboard on the MyTrade MM website and specified how many wash trades they wanted executed each day on named exchanges, a product the firm called “Volume Support.” Bots did the rest, buying and selling the same asset repeatedly to inflate apparent volume. As of October 2024 the service had dozens of clients.

    Zhou was candid with people he believed were prospective customers. MyTrade MM “does self-trades — a buy and a sell in the same second,” he told them, and its volume bot could be used to run pump and dumps. The point, he said, was to draw in “other buyers from the community, people you don’t know about or don’t care about,” because “we have to make [the other buyers] lose money in order to make profit.”

    The FBI built its own token

    Investigators created NexFundAI, a fictitious crypto company complete with a website and an Ethereum-based token that traded on Uniswap until law enforcement disabled it, then used it to solicit market-making services and record what was offered.

    The sting produced charges against 18 individuals and entities in October 2024, including market makers Gotbit, ZM Quant and CLS Global.

    Zhou’s plea agreement required MyTrade MM to stop selling Volume Support and permanently deactivate the bots behind it. It also required the firm to post a notice on its own website stating that volume support is “a form of wash trading and illegal under the laws of the United States.”

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • SEC Bought a Billion Airline Records to Track Travelers—Likely Without a Warrant

    SEC Bought a Billion Airline Records to Track Travelers—Likely Without a Warrant

    In brief

    • SEC documents obtained by 404 Media show the agency subscribed to Airlines Reporting Corporation’s Travel Intelligence Program, which held over one billion ticket records.
    • The data included names, credit card numbers, routes, and an alert system that flagged new bookings by people the agency was monitoring — likely without a warrant.
    • ARC, co-owned by Delta, United, and American, sold the data until lawmaker pressure forced a shutdown in 2025.

    The Securities and Exchange Commission bought access to a worldwide airline ticketing database holding more than one billion records, according to SEC documents obtained by 404 Media through a Freedom of Information Act request.

    The data came from Airlines Reporting Corporation, a clearinghouse co-owned by American, Delta, and United that sits between carriers and travel agencies, and resold bookings made through sites like Expedia and Kayak.

    The records held passengers’ names, the credit cards used to buy tickets, departure and arrival cities, and flight numbers. More than that, the SEC’s subscription included an alert system that checked new bookings against a list of people it was monitoring, flagging travel from the prior 24 hours, with the agency requesting between one and 25 of these alerts a day.

    No court order was needed; the government simply bought the data, likely without a warrant.

    The SEC is a financial regulator, not a spy agency. Its job is to protect American consumers from insider trading, fraud, and market manipulation. But the same travel and payment trail it purchased is exactly the one crypto holders leave behind: a credit card tied to an exchange account, a flight to a conference, a border crossing. When the state can watch both the chain and the boarding pass, the line between market cop and surveillance arm gets thin.

    A year into the second Donald Trump presidency, the SEC has pulled back from major crypto enforcement while the data-broker workaround lets agencies skip the warrant they’d need if they demanded the records directly.

    The IRS has been expanding its own surveillance of crypto investors through the same playbook. The SEC’s Coinbase probe of a year ago showed the same appetite for user data. The question is less whether the SEC wants the information than how it gets it.

    The loophole, again

    Critics call it the data broker loophole: buy what you can’t subpoena. ARC’s Travel Intelligence Program sold the same post-9/11 surveillance infrastructure to the FBI, IRS, and Homeland Security before pressure from lawmakers forced its shutdown in 2025.

    The newly released documents show its reach was wider than known—foreign-to-foreign journeys sat in the system alongside domestic ones.

    ARC defended the program. The company told 404 Media that TIP “was established after the September 11, 2001, terrorist attacks” and “has likely contributed to the prevention and apprehension of criminals involved in… money laundering” and terrorism. Money laundering is the charge crypto draws most often.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • Putin Signs Russia’s First Crypto Law: Trading Is Legal, Payments Stay Banned

    Putin Signs Russia’s First Crypto Law: Trading Is Legal, Payments Stay Banned

    In brief

    • President Vladimir Putin signed Russia’s first law giving comprehensive rules to crypto exchanges, custodians, brokers, and mining.
    • Only firms on a state registry may run exchanges after July 1, 2027, with a 15 million ruble ($187,000) capital floor and a self-regulatory body requirement.
    • Using crypto as money is still banned, and banks can block transfers they suspect flow to unregistered providers.

    Russian President Vladimir Putin signed the country’s first comprehensive law governing digital currencies on Tuesday, state news agency Tass reported. The legislation sets rules for how crypto is issued, stored, accounted for, and traded, wrapping exchanges, digital depositories, brokers, and clearing houses into one framework.

    It isn’t a free market. The law keeps the ban on using crypto and digital rights as payment for goods and services, and it blocks advertising that pitches crypto payments. Russia already legalized cryptocurrency mining in 2024, when Putin signed a separate bill green-lighting the industry, so this law fills the gap on trading and custody that the mining rules left open.

    How the market gets built

    Only organizations on a special government registry may run crypto exchanges, and existing operators get a grace period to register by July 1, 2027. Registered exchanges need at least 15 million rubles (about $187,000) of their own capital and must join a self-regulatory body in the financial market.

    Regular exchange activity kicks in once a firm trades more than 3.5 million rubles in a month. Banks and foreign-lender branches must reject transfers they suspect are routed through an unregistered provider.

    Retail access is capped and gated. Non-accredited investors may buy the most liquid cryptocurrencies (list to be disclosed) through licensed intermediaries, up to 300,000 rubles per year per intermediary, and both retail and qualified investors must pass a knowledge test. Qualified investors face no purchase limit.

    The law also guarantees court protection for crypto owners regardless of whether they declared the assets before.

    Most of the provisions take effect September 1. Decrypt tracked the bill as it neared passage, noting the gap between “buy crypto” and “use crypto” was the whole point—Russia wants a regulated on-ramp, not a parallel currency. The framework dovetails with the digital ruble push, which the central bank governor says banks must support by the same September 1 date.

    The sanctions question

    The law’s exceptions matter most outside Russia. Settlements under foreign trade contracts between residents and nonresidents are permitted, as are deals involving mined coins and payments inside digital asset platforms. That carve-out is the part Western regulators will watch: Russia has leaned on crypto for cross-border trade as sanctions pressure built.

    The law gives Russian holders something they didn’t have: legal standing and a licensed venue. It gives the state what it wanted more: a central bank-supervised pipeline it can monitor.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • Bitcoin AI Security Audit Files 4,962 Findings Across 390 Projects

    Bitcoin AI Security Audit Files 4,962 Findings Across 390 Projects

    In brief

    • Cashu creator calle said the campaign logged 85 critical and 635 high-severity issues in its first 30 hours.
    • Contributors each prompt their own agents, which the group says produces a wider spread of hits than a single method would.
    • Privacy and coinjoin projects carried the highest share of serious findings, at 24%.

    A volunteer group calling itself the Bitcoin Red Team has filed 4,962 security findings across 390 Bitcoin projects in roughly 30 hours, running what it describes as a “large-scale ecosystem audit” with AI agents doing much of the scanning.

    Pseudonymous developer calle, who created the Bitcoin ecash protocol Cashu, published the campaign’s first situation report on Wednesday. It puts 85 findings at critical severity and 635 at high, together 14.5% of the corpus and an average of 1.85 serious issues per project, filed at 166 findings an hour. He said the team has grown to 16 people working around the clock; the report logs 17 contributors, 14 of them human and three automated.

    Much of the work is still manual, “hand holding the AI,” calle wrote, though automated harnesses are improving, and 91% of findings arrived through automated scan intake. Letting everyone use their own preferred review method “has proven to be the most effective strategy,” he said, because contributors prompt their agents differently and turn up different bugs. Around 21% of findings have been dynamically reproduced with proof-of-concept code.

    The severity spread varies sharply by category. Privacy and coinjoin tools returned the highest proportion of high-or-critical findings at 24%, followed by swaps and exchanges at 21% and payments and merchant tools at 17%. Cryptographic libraries and SDKs produced the largest raw volume at 1,101 findings, but only 10% cleared the high bar.

    Maintainers are getting flooded

    Only 19 projects, under 5% of those reviewed, have had findings disclosed upstream so far, and calle acknowledged the campaign is adding to a difficult moment for maintainers.

    “We’re sincerely sorry if our reports added stress to your already stressful day,” he wrote, while arguing the findings should go out fast because project owners are best placed to validate them, validation is now nearly free with AI, and anyone else running the same tools will reach the same bugs. Eight findings have been retired as false positives.

    The Coldcard backdrop

    The campaign lands as Bitcoin’s security assumptions come under scrutiny. Coinkite’s Coldcard wallet lost users some $130 million after a March 2021 firmware build drew wallet seeds from a software fallback rather than the device’s hardware random number generator, leaving private keys guessable. In a post-mortem, the firm noted it was likely that “someone used AI to review previous versions of our firmware.”

    Ledger chief technology officer Charles Guillemet told Decrypt on Tuesday that the incident showed AI was now being used to identify vulnerabilities in crypto code “at machine speed.” He added that “open source and reviewed are not the same thing,” noting the Coldcard flaw sat in public code for more than five years until an adversary reportedly used AI to find it. Defence, he argued, now has to move at the same speed as attackers—as groups like the Bitcoin Red Team are demonstrating.

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.
  • Meta Debuts AI Coding Agent Muse: Here’s How It Compares to Claude Code and Codex

    Meta Debuts AI Coding Agent Muse: Here’s How It Compares to Claude Code and Codex

    In brief

    • Meta released Muse Code (beta), a terminal coding agent powered by Muse Spark 1.2, its updated coding model. It’s available now via the Meta Model API and a curl install script.
    • The agent coordinates persistent background subagents and keeps a replay-exact event log, so a crash resumes exactly where it stopped.
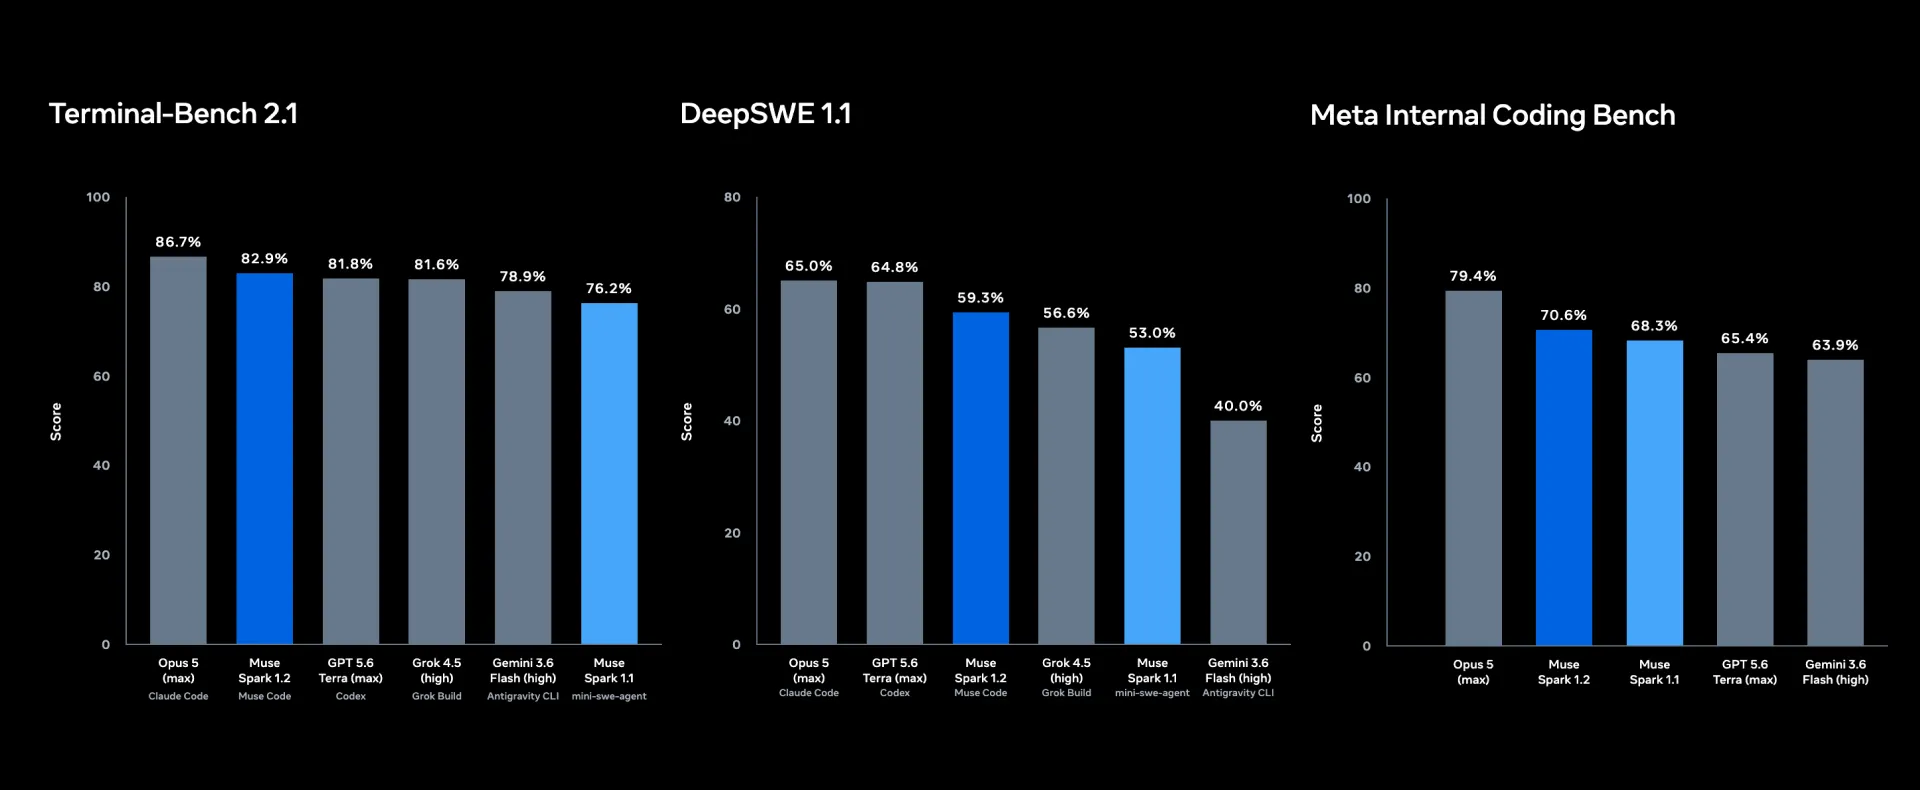
    • On Meta’s own charts, Muse Spark 1.2 trails Anthropic’s Opus 5 on every coding benchmark shown, while beating OpenAI’s Codex and Google’s Antigravity on most.

    Meta is the latest tech giant to ship a coding agent, racing to compete with leading AI behemoths Anthropic and OpenAI.

    “We’re excited to release Muse Code (beta), a terminal coding agent powered by Muse Spark 1.2, our newest model,” the company wrote in an official announcement. “This marks our next step toward the frontier, with larger and much more capable models on the way.”

    As an agentic coding tool, Muse Code is built for software engineering across large repositories. Per Meta, it “takes on complex software engineering tasks across large repositories: planning changes, writing code, and validating the results. It can coordinate multiple persistent subagents for each task, solving difficult problems faster, more accurately, and with less intervention.”

    The detail that stands out is the runtime. Muse Code logs every model call, tool run, approval, and edit to a local event log that acts as a single source of truth. “This single source of truth makes the runtime replay-exact and restart-safe: after a crash, the agent can resume precisely where it stopped,” Meta said. For long-running jobs, that’s the feature that matters more than raw speed—and it’s the part competitors haven’t made a selling point.

    It also ships with default skills. The “/plan” command turns a task into an approval-gated plan, while “/grill” stress-tests that plan until it holds up and “/goal” works toward successful completion of the objective similar to what Hermes does. Meta said it co-trained Muse Spark 1.2 with Muse Code so the core LLM and the agent work together in synergy.

    The benchmarks, and the catch

    Muse Spark 1.2 is a coding-focused update to Muse Spark 1.1. Meta said it “significantly scaled up training compute on coding tasks while expanding training environment diversity, delivering improvements in code generation, complex debugging, and end-to-end developer workflows.” The charts tell a clear story.

    On Terminal-Bench 2.1, Muse Spark 1.2 with Muse Code scored 82.9%, behind Claude Code on Opus 5 at 86.7% but ahead of GPT-5.6 Terra on Codex (81.8%) and Grok Build (81.6%).

    DeepSWE 1.1, which measures agentic coding capabilities, was closer: 59.3% for Muse versus 65.0% for Opus 5 and 64.8% for Codex. On Meta’s internal coding bench, Muse hit 70.6% to Opus 5’s 79.4%.

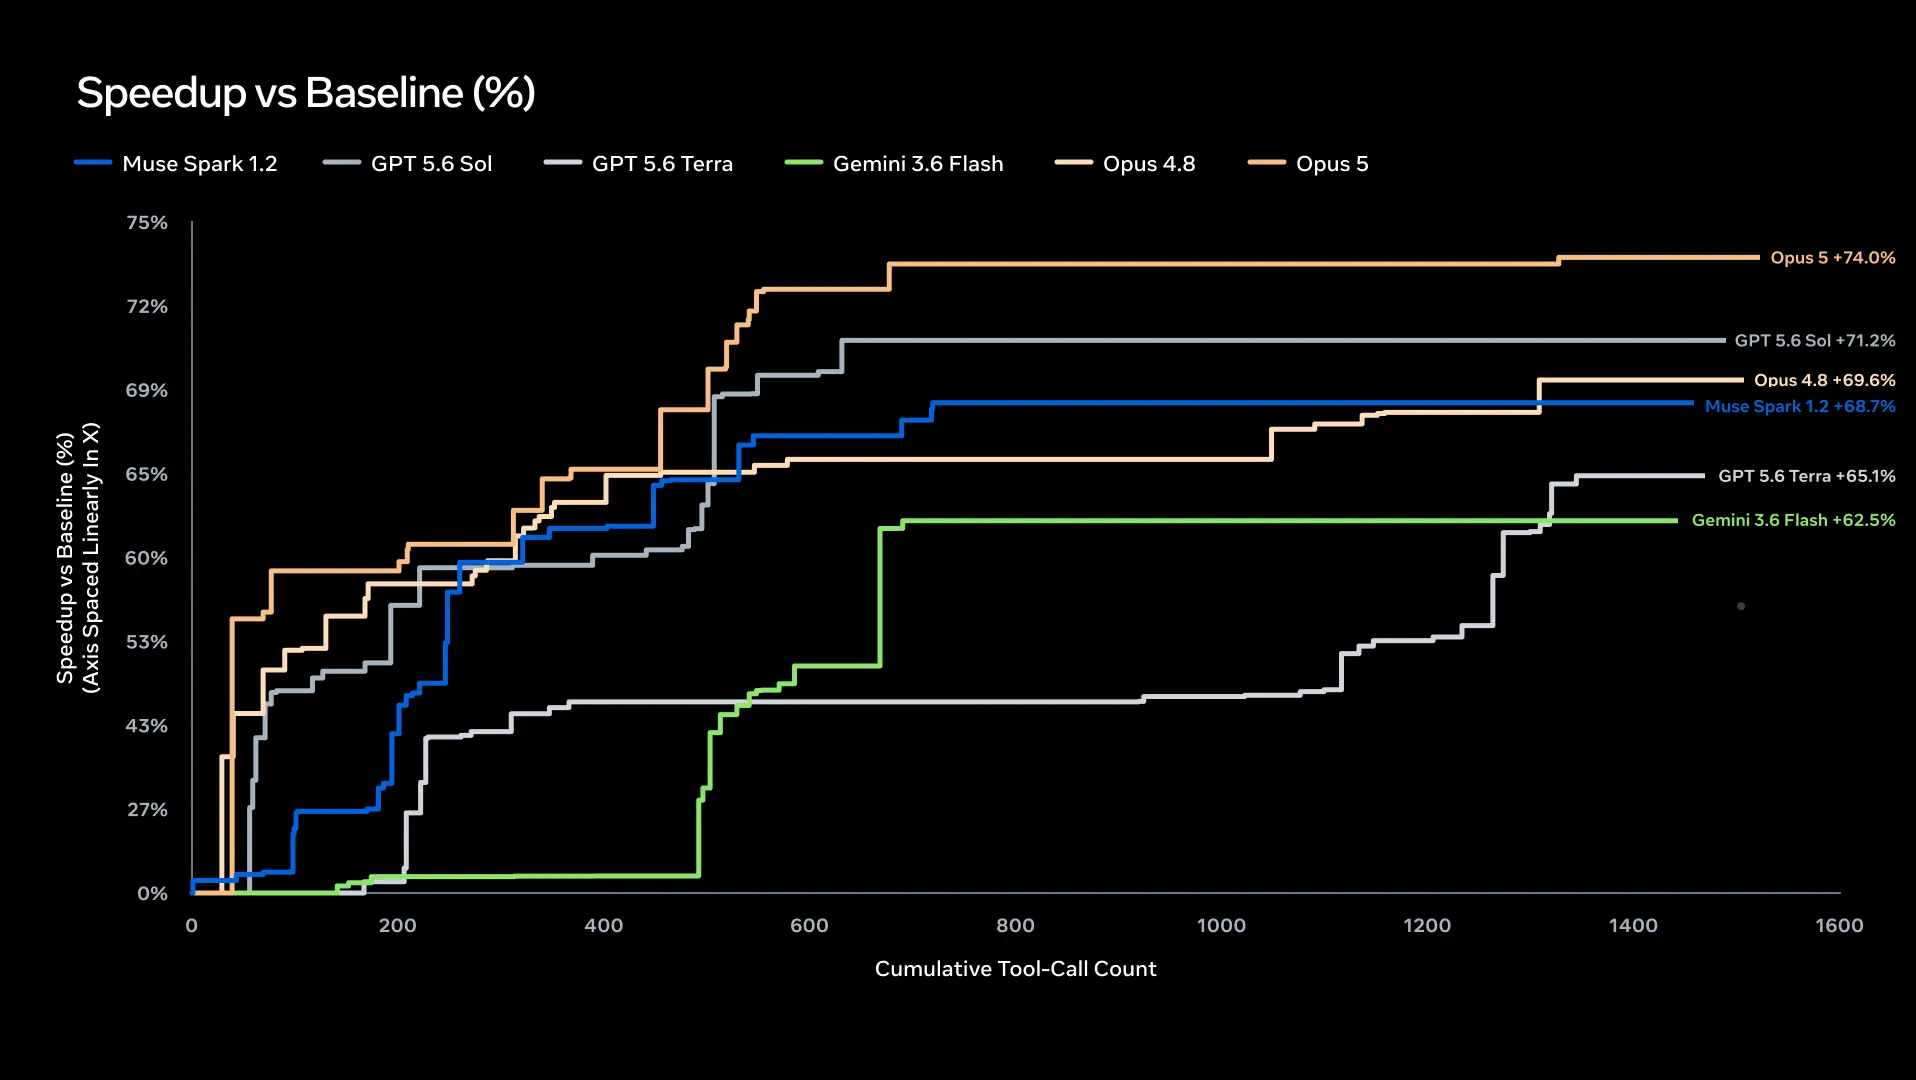
    The speedup charts flip the order. Over 1,000-plus tool calls, Opus 5 posted the biggest gain versus baseline (about 74–75%), with Muse Spark 1.2 mid-pack at roughly 61–69% depending on the run. Meta’s point is that the agent keeps improving as tool calls accumulate, the behavior you want from a long-horizon coder.

    The most interesting demos are long-horizon and multimodal. In stress testing, Meta said Muse Code “iteratively optimized GPU kernels over 1,000+ tool calls (up to 24 hours) on Nvidia Hopper GPUs.” That means it was able to improve over time.

    There’s also a visual-coding angle. In one demo, a user drops a fly-through video of a house into the terminal as an mp4, and Muse Code “interprets the video and produces a visually rich website with booking capabilities.” Reading raw video into a working web app is the multimodal pitch Meta has been making across the Muse line.

    See the launch thread:

    The field is already crowded

    That said, Meta is late to the fight. OpenAI’s Codex already runs parallel cloud agents; DeepSeek has built its own rival to Claude Code and agentic tools like Hermes or OpenClaw are already good substitutes with more capabilities. Muse Code’s edge is the crash-safe runtime and the subagent design, not benchmark supremacy.

    The risk is the usual one for agentic coding: an agent that resumes after a crash and keeps calling tools for 24 hours is powerful and unpredictable. Meta is betting developers want that autonomy, and it’s shipping now.

    Muse Code is available for testing upon installation entering this command:
    curl -fsSL https://dev.meta.ai/install.sh | bash

    Daily Debrief Newsletter

    Start every day with the top news stories right now, plus original features, a podcast, videos and more.