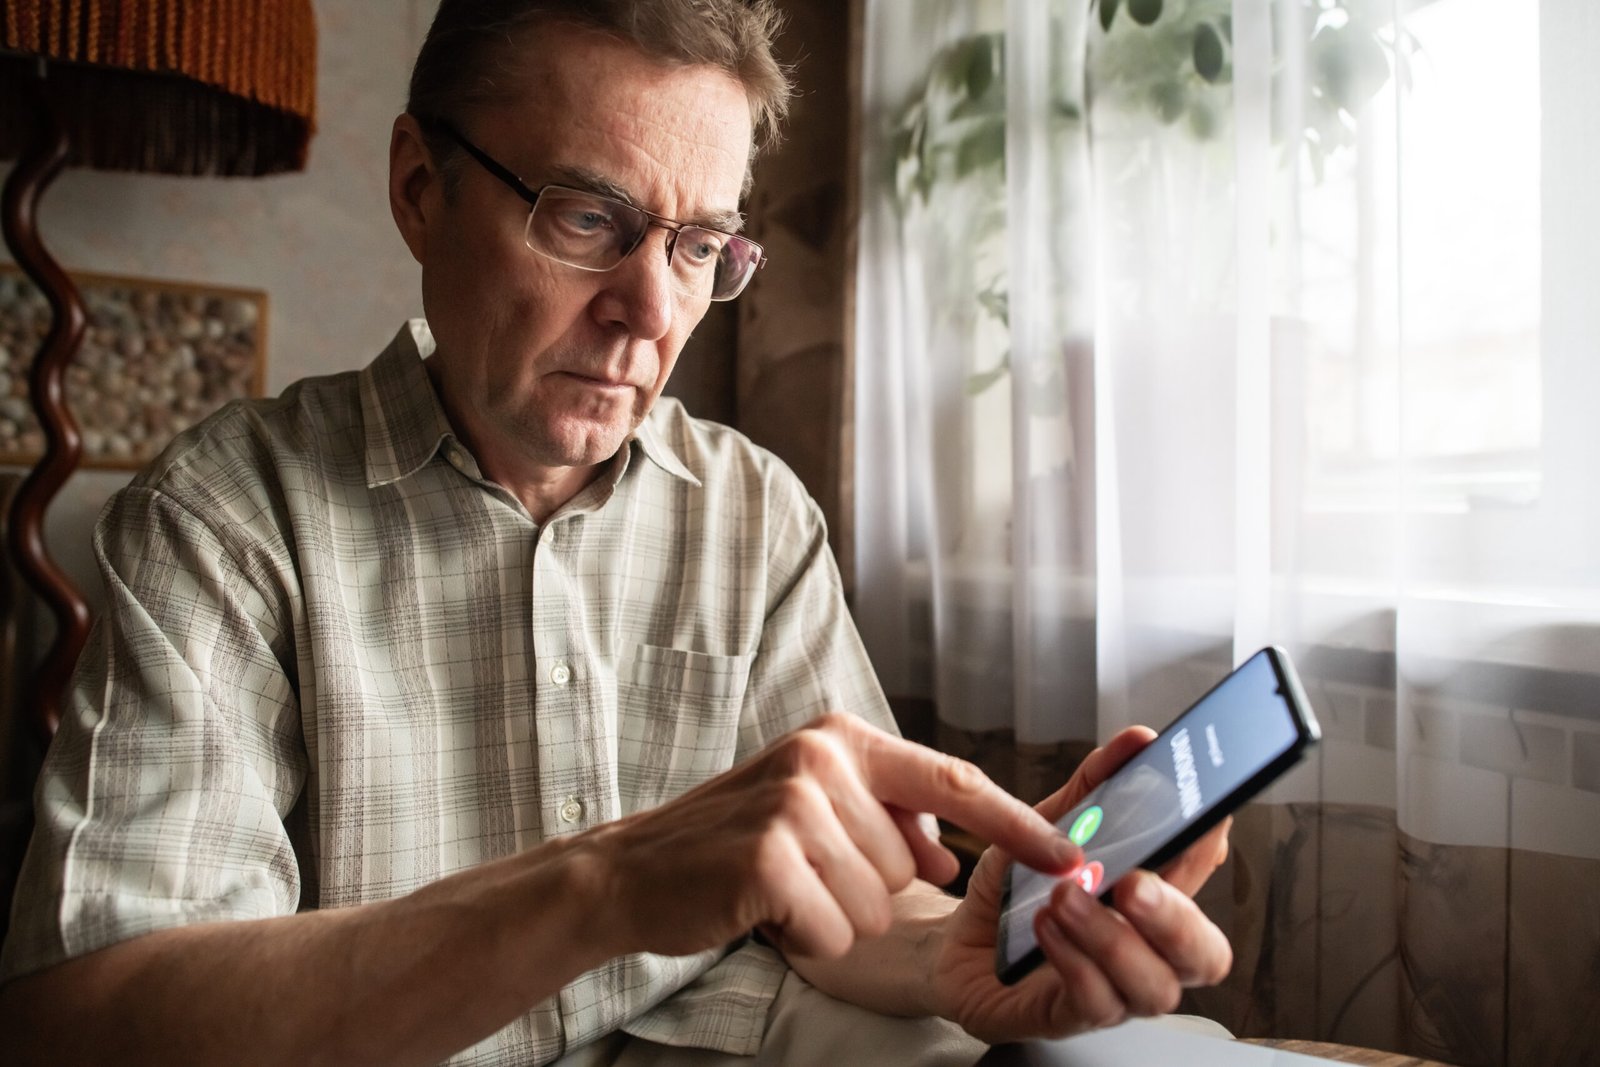
In an era when AI-assisted scams run rampant on social media, gaming platforms, and even within ads on legit websites, learning how to protect elders and other family members from online threats is more important than ever. October is cybersecurity awareness month, which is why, for PCMag’s cover story, I wrote about online scams affecting older people. I interviewed several experts for this piece and examined the story of a retiree who lost almost everything to online scammers posing as federal agents.
While my story focuses on seniors, it’s important to remember that scammers target everyone, regardless of age. In fact, according to a recent CNET Group survey (which includes PCMag, Mashable, ZDNET, and others), more than 60% of Americans consider AI-assisted scams a greater threat than malware.
Preventing scams from happening is a lot easier than recovering your money after a scam occurs. When you take time to lock down your online presence, pay attention to what you’re clicking on or responding to when completing tasks online, stay focused and skeptical when reading news and social media posts, and keep your accounts protected with multi-factor authentication, you make it a lot harder for scammers to turn you into a victim.
In other security news this week, a former OpenAI employee accused of using a recording device to spy on company executives has a lot of support from a surprising source. According to federal prosecutors, 35-year-old Abdulrahman Alfozan, a former engineering lead and Saudi national, was in frequent communication with a member of the Saudi royal family. Prosecutors in the US are submitting evidence about his potential motives.
Rounding out PCMag’s security coverage this week is a reminder to back up your phone before you fly overseas. US border agents can search your phone when you return. If your solution to a search is to wipe your phone, think again. In some circumstances, if you choose to erase your phone too late, you can wind up in jail. Before you fly the friendly skies, read our guide to prepping your phone for a border crossing.
Let’s take a look at what else is happening in the infosec world this week.
Weak Encryption Keys Trigger Heartbleed-Level Security Cleanup
This week, browser makers and major app publishers are on high alert after blocking eight intermediate certificates, all from India-based company eMudhra Limited. The eMudhra keys are exceptionally weak and could be used to sign browser and app credentials for any site. There are no official reports of the keys being used maliciously, but the real headache is the cleanup process, which will involve tracking down the certificates used in Linux distributions or internet-of-things devices and could take years to complete. Experts have likened the anticipated recovery process to the one following the discovery of the Heartbleed vulnerability, which led to thousands of compromised servers in 2014.
Burger King Japan Breach Exposes Data of 11 Million Customers
I always tell readers to refrain from downloading unnecessary apps, and here’s why: Companies can’t or won’t keep your data safe. In the latest example of this phenomenon, Burger King’s Japanese division disclosed a data breach that exposed the email addresses, names, phone numbers, dates of birth, genders, and places of residence of 11 million customers. That’s all data that hackers, scammers, and criminals of all kinds can use to create convincing phishing emails or text messages to trick you into giving them your money, additional personal data, or both.
In an official notice, Burger King Japan apologized for the breach but didn’t identify the attackers or explain how it happened. The company says it’s working with third-party security specialists to find out more details.
Sextortion ‘Help’ Firm Took $60 Million From Victims, FTC Alleges
The FTC alleges that Digital Forensics Corporation and its owner Dmitry Belkin tricked sextortion victims into paying millions of dollars for services they didn’t provide. If you’re unfamiliar with how sextortion works online, here’s a quick rundown: When a criminal possesses intimate photos, videos, or other sensitive materials of another person, they may threaten to share the media unless the victim complies with their demands. Sometimes the scammer wants money from the victim; other times, they want more explicit content. These demands can become expensive, stressful, or embarrassing for victims, who, in desperation, turn to the internet for help.
Apparently, Digital Forensics advertised its services on Google, YouTube, X, and similar platforms, and made claims that it could track down sextortionists and assist law enforcement with evidence that could lead to arrests. Instead, the company apparently just blocked sextortionists from the victims’ accounts, created fake chat transcripts, and always showed the sextortionists in the same locations, usually Nigeria or the Philippines. Digital Forensics charged between $1,499 and $20,000 for the fraudulent assistance packages. The allegations against the company haven’t gone to court yet.
Recommended by Our Editors
If you ever find yourself in a sextortion or blackmail situation, remember to document everything. Take screenshots of all threats, messages, and demands, and then block the person who is threatening you. Do not delete your account or messages, as law enforcement may need them later. You should then report the crime to local law enforcement or the FBI. After that, get support from someone you trust. Telling someone what happened can help you make decisions about handling the situation that keep you out of the clutches of a scammer who is trying to make a quick buck off of someone else’s pain.
Ask Our Expert: Can My Spouse and I Share One Hardware Security Key?
Do you have a question about online privacy or security? I’m here to help! You can submit your question here, and I may answer it in an upcoming SecurityWatch column and newsletter. If you’re not subscribed to the newsletter, head here to sign up, and check back each week for the latest updates from PCMag’s security team. Now, on to this week’s question!
Stephen G asks: “Do I need to buy separate hardware security keys for me and my wife? We keep separate accounts.”
Hi Stephen, thanks for reading! Yes, each of you will want your own hardware security key. You’ll need to use the key each time you authenticate your identity for your online accounts, including email, banking, social media, and streaming services, so keep it with you when you’re out and about. A hardware security key stores a private cryptographic key that only unlocks your account, so it’s not something you can share between two people who use different accounts. The good news is that most keys are small enough to hang on a standard keychain, or you can keep it in your wallet.
About Our Expert

Kim Key
Senior Writer, Security
Experience
I review privacy tools like hardware security keys, password managers, private messaging apps, and ad-blocking software. I also report on online scams and offer advice to families and individuals about staying safe on the internet. Before joining PCMag, I wrote about tech and video games for CNN, Fanbyte, Mashable, The New York Times, and TechRadar. I also worked at CNN International, where I did field producing and reporting on sports that are popular with worldwide audiences.
In addition to the categories below, I exclusively cover ad blockers, authenticator apps, hardware security keys, and private messaging apps.
Leave a Reply